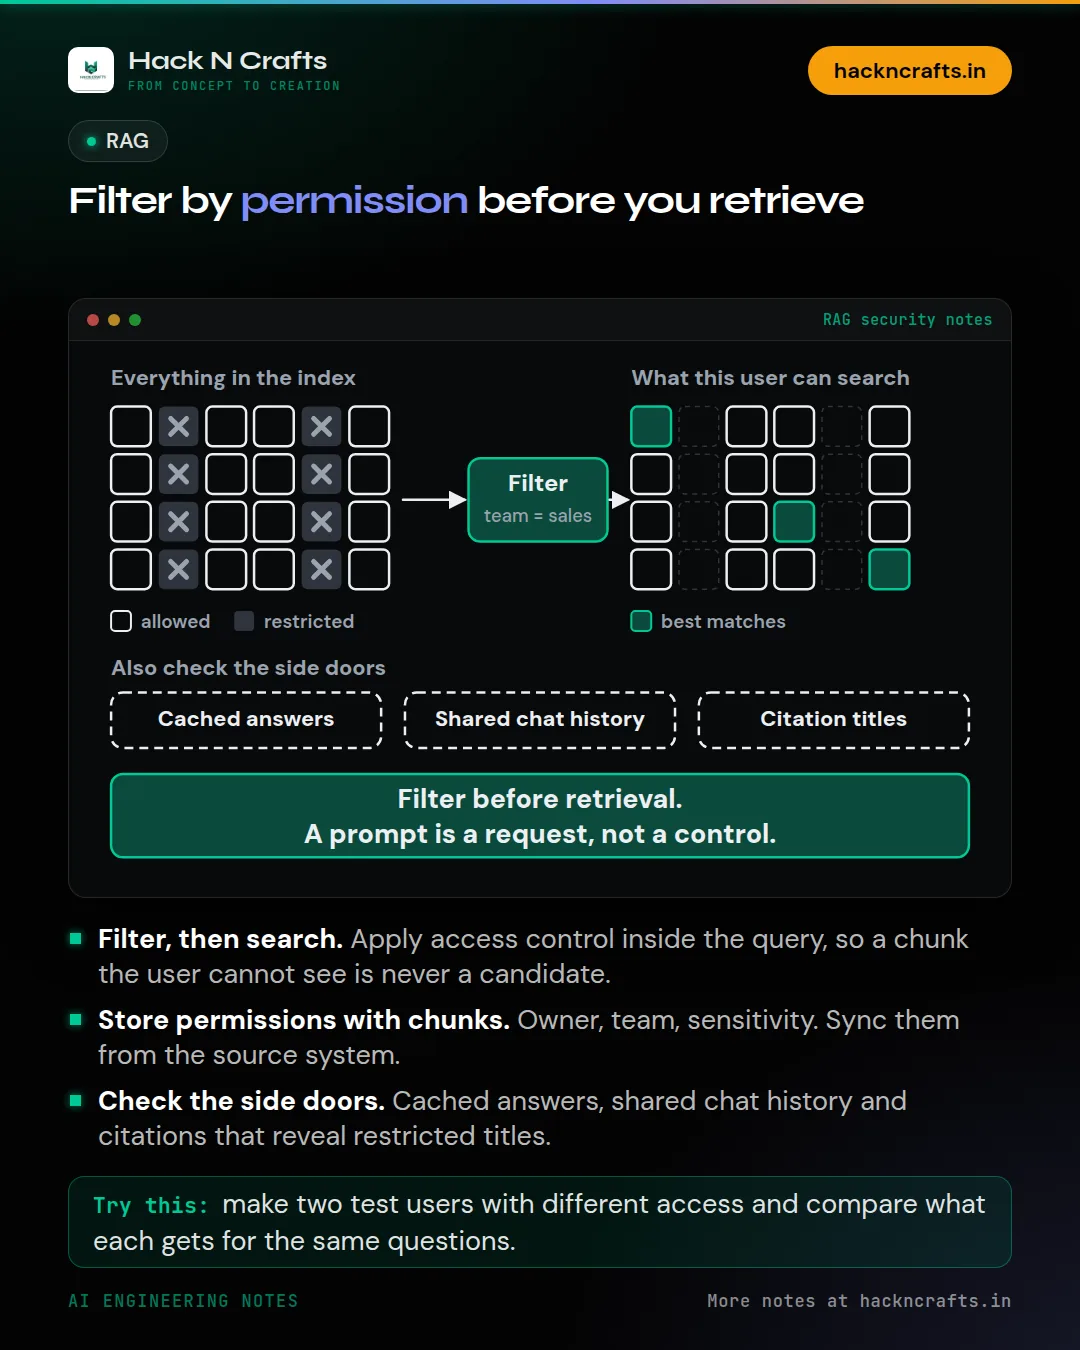
Filter by permission before you retrieve
The scariest RAG bug isn't a wrong answer. It's a right answer from a document the user was never allowed to see.
It happens when everyone's documents go into one index and the model gets whatever matches best. The retriever doesn't know about permissions. It only knows about similarity.
The rule: filter before retrieval, not after. Access control belongs in the query, so a chunk the user can't see is never a candidate.
How to do it:
- 1Store the permission data with every chunk: owner, team, sensitivity, whatever your system uses.
- 2Pass the user's identity into the search and apply a metadata filter inside the vector or hybrid query.
- 3Keep the source of truth for permissions in the original system, and sync it. A copy that goes stale will leak.
- 4Don't rely on the prompt. 'Only answer from documents the user can access' is a request, not a control.
Also check the side doors: cached answers, shared conversation history, and citations that reveal the titles of restricted files.
Test it the way an attacker would. Make two test users with different access, ask both the same questions, and compare what comes back.
What would happen if an intern asked your RAG app about salaries?
New notes go out on LinkedIn first. Building something with AI? We can help.